As enterprises scale across physical branches, complex supply chains, and distributed workforces, operational risks multiply exponentially. When internal control architectures fail to keep pace, organizations face severe vulnerabilities: fraud, financial shrinkage, regulatory penalties, and brand erosion.
This is where internal audit acts as the primary governance shield for the modern enterprise, safeguarding not only financial ledgers but operational, procedural, and compliance integrity.
What defines an effective internal audit framework? What are its primary types and phases, and how does dedicated digital audit software streamline execution?
What Is Internal Audit?
According to the Institute of Internal Auditors (IIA), internal audit is an independent, objective assurance and consulting activity designed to add value and improve an organization’s operations.
While traditional inspection models focused narrowly on post-mortem fault-finding, modern internal audit operates as a forward-looking discipline: anticipating institutional risks, closing control gaps, and driving continuous operational improvement.
Core Objectives of Internal Audit
A mature internal audit program delivers 4 fundamental governance pillars:
Safeguarding Enterprise Assets: Protecting physical, financial, and digital assets (cash, inventories, equipment, intellectual property) from fraud, waste, and loss.
Operational Efficiency & Standardization: Ensuring consistent execution of Standard Operating Procedures (SOPs) and corporate policies across all business units.
Statutory & Regulatory Compliance: Guaranteeing strict adherence to statutory laws, labor codes, environmental standards, and data privacy mandates (GDPR, ISO).
Data Integrity & Reporting Reliability: Providing Executive Leadership and Audit Committees with uncompromised, tamper-proof operational and financial intelligence.
Primary Types of Internal Audits
Internal audits are categorized according to their operational scope:
1. Compliance Audit: Evaluates institutional adherence to external statutory mandates, industry regulations, and internal corporate policies.
2. Operational Audit: Evaluates the systematic efficiency, resource allocation, and procedural consistency across frontline branches, warehouses, and plants.
3. Financial Audit: Reviews accounting ledgers, cash register management, invoicing workflows, and balance sheet integrity.
4. IT & Cybersecurity Audit: Audits digital infrastructure, access privileges, data encryption, disaster recovery, and cybersecurity protocols.
5. Process Audit: Analyzes end-to-end organizational workflows—such as procurement, logistics, HR onboarding, and quality assurance—to eliminate operational bottlenecks.
The 4 Phases of the Internal Audit Lifecycle
A standardized internal audit lifecycle follows a systematic 4-stage workflow:
[ 1. Planning & Risk Scoping ] ➔ [ 2. Fieldwork & Evidence ] ➔ [ 3. Executive Reporting ] ➔ [ 4. Follow-up & CAPA ]
Planning & Risk Assessment: Mapping the audit universe, prioritizing high-risk operational entities, and configuring standardized audit workpapers.
Fieldwork & Evidence Gathering: Auditors perform physical walkthroughs, evaluate sample records, interview operational leads, and capture field observations.
Reporting & Executive Presentation: Findings, control deficiencies, and severity rankings are compiled into executive compliance summaries.
Remediation & Closed-Loop Follow-Up: Corrective and Preventive Actions (CAPA) are assigned to operational process owners, tracking remediation to verified closure.
The Failure of Legacy Internal Audits
Historically, internal audits relied on manual paperwork, disconnected spreadsheets, and fragmented email trails. This legacy approach introduces critical vulnerabilities:
Weeks lost compiling manual reports after site visits,
Risk of fraudulent "desk audits" where inspectors complete forms off-site,
Unresolved findings languishing in spreadsheets without remediation.
Modernizing Internal Audits with Denetrium
Denetrium bridges executive strategy with frontline verification through specialized audit software and a robust mobile audit application:
Frontline Mobile Audits: Field auditors execute structured checklists via mobile phones and tablets in real time.
Geofencing & Tamper-Proof Timestamps: GPS geofencing and mandatory live camera captures eliminate off-site audit fabrication.
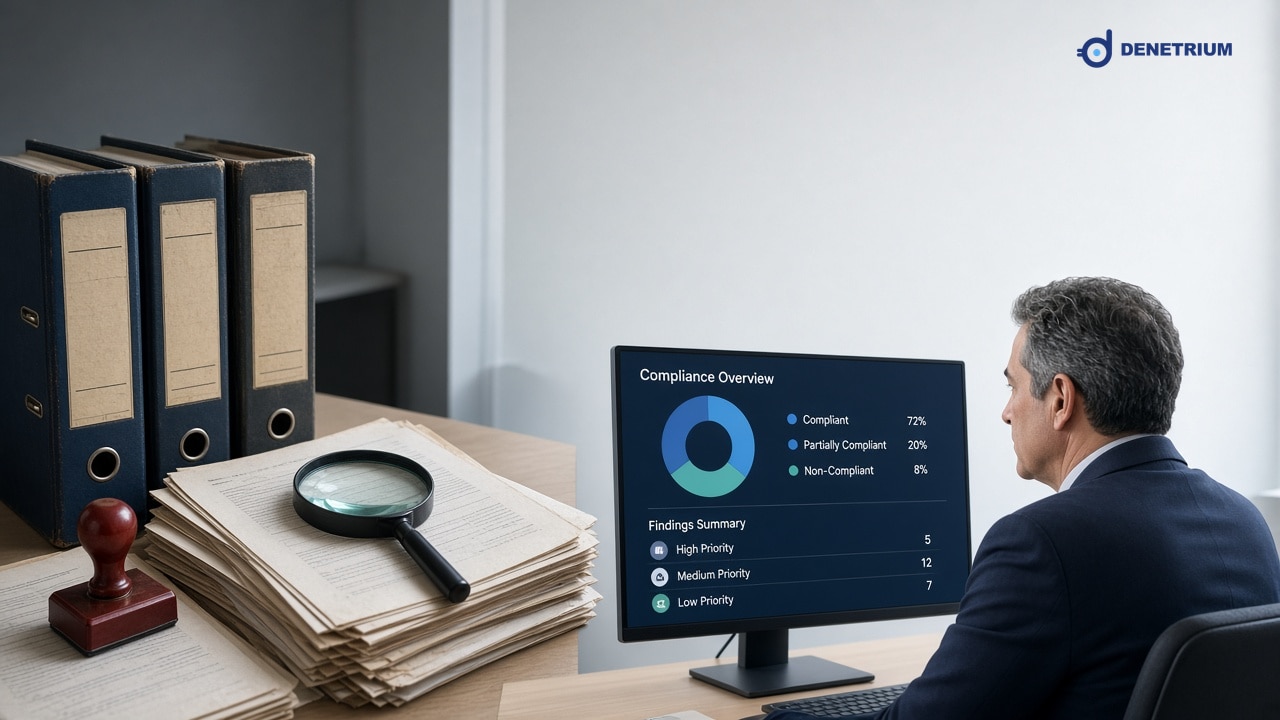
Instant Board-Ready Reporting: Comprehensive, formatted PDF compliance dossiers populate the executive dashboard the second fieldwork concludes.
Closed-Loop CAPA Engine: High-severity findings trigger automated corrective tasks; assignees cannot close tickets without uploading verified photographic proof.
Enterprise Risk Dashboards: Benchmark regional units, track recurring failure patterns, and visualize organizational compliance indexes from a single command console.
Do not leave your internal audit governance to outdated spreadsheets and paper binders. Deploy Denetrium’s internal audit and digital audit platform to transform your audit function into an agile, data-driven engine of operational excellence.