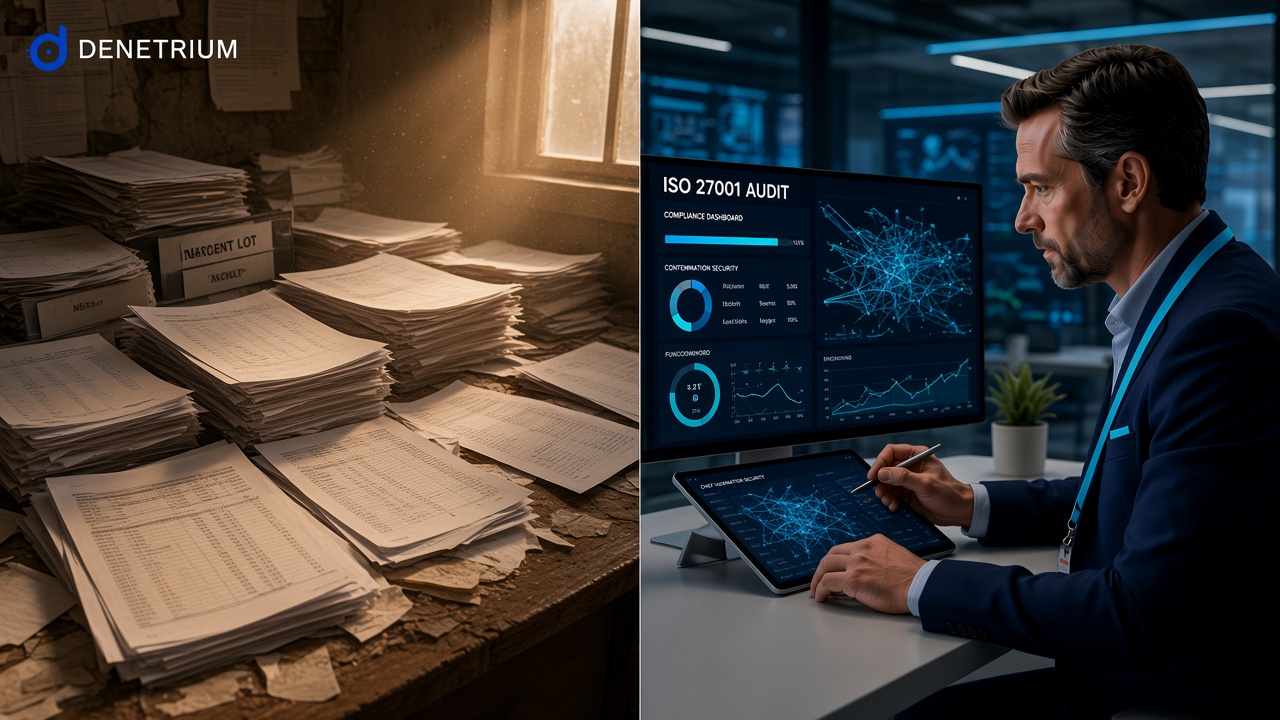
In today’s digital economy, an enterprise’s most valuable yet fragile asset is its proprietary data. Customer databases, intellectual property, financial records, and source code are rarely compromised solely by sophisticated external cyber exploits; more frequently, breaches originate from mundane physical vulnerabilities, unverified access privileges, or neglected procedural controls. The globally recognized ISO/IEC 27001 Information Security Management System (ISMS) standard was engineered to neutralize these exposures systematically.
However, across many organizations, ISO 27001 compliance remains static and disconnected:
Information asset registers and threat-risk matrices sit trapped in outdated, unencrypted spreadsheets,
Routine enforcement of "Clean Desk and Clear Screen" policies, server room access logs, and visitor escorts rely on neglected paper sign-in clipboards,
Third-party software vendors and outsourced infrastructure providers operate without continuous, structured security audits,
When independent external audit applications or certification assessors arrive, IT and security personnel waste weeks retroactively compiling compliance evidence across 93 Annex A controls.
True information security cannot be sustained through static annual reviews. Modern cyber and physical resilience demands an agile digital audit software platform that automates evidence collection, verifies ground controls, and enforces closed-loop remediation.
Here is how Denetrium’s enterprise audit tracking program, online audit, and mobile audit application modernize ISO 27001 governance across 5 core pillars:
1. ISO/IEC 27001:2022-Aligned Annex A Dynamic Checklists
The updated ISO 27001 standard consolidates controls into 4 streamlined domains: Organizational, People, Physical, and Technological controls across 93 specific checkpoints.
The Denetrium Approach: Leverage pre-built, standardized inspection catalogs mapped directly to ISO 27001:2022 clauses.
Checkpoints connect seamlessly to targeted controls (e.g., A.7.7 Clear desk and clear screen, A.7.4 Physical security monitoring, A.5.19 Information security in supplier relationships), turning field observations into instant, verifiable compliance proof.
2. Physical Data Center and Facility Security Mobile Audits
Cybersecurity fails if physical security collapses. Unlocked server racks, obstructed emergency fire suppression nozzles, or blind spots in CCTV surveillance undermine your ISMS perimeter.
The Denetrium Approach: Internal auditors and security leads inspect server rooms, biometric access turnstiles, and network closets using the native mobile audit app.
Enforced GPS geofencing, cryptographic timestamps, and live camera captures guarantee physical presence inside the data facility, eradicating fabricated desk audits.
3. Asset-Centric Threat Profiling and Risk Mapping
Not all enterprise assets share identical threat profiles; customer databases, edge servers, and development repositories require differentiated control rigor.
The Denetrium Approach: Link dynamic inspection programs directly to your centralized IT asset inventory.
Any observed control gap—such as an unpatched network switch or an unencrypted external storage unit—dynamically escalates that asset’s vulnerability index across the CISO’s executive command console.
4. Incident Remediation Powered by Closed-Loop CAPA Discipline
When a security vulnerability is identified, delayed remediation exposes the organization to immediate exploitation.
The Denetrium Approach: Any control non-conformity triggers an assigned, deadline-tracked Corrective and Preventive Action (CAPA) ticket.
Assignees must complete structured 5-Why root-cause analyses and upload verified technical documentation or screenshots demonstrating remediation. Tickets cannot be closed without digital sign-off from the Lead Security Auditor.
5. Continuous 365-Day Readiness for External Audits and Regulators
Eliminate the frantic scramble for historical logs when third-party certification bodies or statutory privacy authorities (GDPR, KVKK) initiate inspections.
The Denetrium Approach: Internal audit workpapers, user access certification reviews, and vendor due diligence dossiers are securely stored and encrypted in the cloud with tamper-proof audit trails.
Generate official ISO 27001 compliance packages with one click, proving your organizational security posture during internal audit and external assessments.
Do not leave your intellectual property and compliance standing to fragile spreadsheets. Deploy Denetrium’s audit software, online audit engine, and audit tracking program to maintain 365-day security, operational resilience, and verified compliance across all business units.