Governance, Risk, and Compliance (GRC) management is no longer an administrative checklist; it is the core foundation of enterprise resilience. Yet organizations seeking audit and risk management software typically encounter two frustrating extremes:
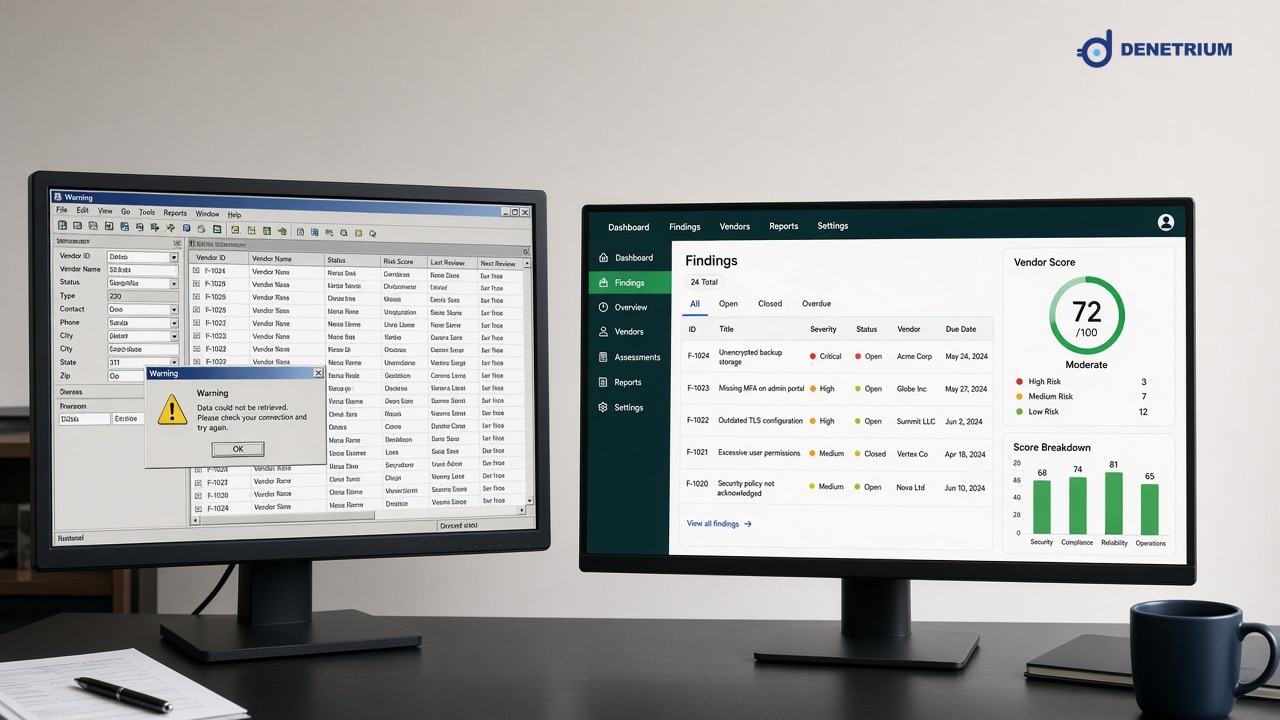
Legacy, bloated enterprise GRC suites requiring year-long implementations, prohibitive licensing fees, and complex workflows that stifle agility,
Disconnected, manual tracking methods that trap audit findings, vendor due diligence, and risk registers inside scattered spreadsheets and lost email threads.
Furthermore, traditional GRC tools remain confined to executive boardrooms; the moment audit requirements hit physical branches, distribution centers, or supplier plants, legacy systems break down.
Denetrium delivers the analytical depth required by Chief Audit Executives and risk directors while stripping away enterprise bloat through an agile, modular architecture.
Here are the 5 core strategic pillars Denetrium’s audit software and digital audit platform bring to internal audit and risk teams:
1. End-to-End Internal Audit Lifecycle Management
Internal audit requires an unbroken operational thread from annual planning and engagement scoping to field workpapers and final board deliverables.
The Denetrium Approach: Structure audit work programs, control testing, and sample criteria from a centralized workspace.
Ground observations link directly to audit workpapers, compiling board-ready executive summaries and deficiency indexes automatically the moment field testing concludes.
2. Ending Unresolved Findings: Closed-Loop Follow-Up & Action Tracking
Uncovering a control failure during an audit is only half the mandate; institutional value comes entirely from verifying remediation.
The Ground Reality: Auditors wasting hundreds of hours sending manual follow-up emails, asking branch managers whether open recommendations have been addressed.
The Denetrium Approach: Every finding spawns an automated remediation ticket assigned directly to the business process owner with firm deadlines. Supported by automated push notifications, SMS, and email escalations, tasks cannot be dismissed without photo verification or signed technical documentation.
3. Operational Risk & Control Mapping (Micro-GRC)
Risk registers must reflect live operational conditions rather than theoretical annual reviews.
The Denetrium Approach: Map operational risks and mitigation controls directly to standardized online audit questionnaires.
Recurring non-conformities identified in the field continuously update risk heatmaps, providing leadership with real-time insight into emerging exposure across the network.
4. Third-Party Vendor Risk & External Audit Governance
Enterprise compliance depends heavily on the integrity of third-party vendors, suppliers, and outsourced service providers.
The Denetrium Approach: Execute vendor onboarding assessments, due diligence audits, and periodic SLA compliance reviews inside a single hub.
Provision secure, role-restricted access to independent third-party auditors and external certification surveyors to coordinate compliance dossiers seamlessly.
5. Modular, Cloud-First Architecture with Frontline Verification
Organizations should not endure months of professional service engagements just to launch an audit workflow.
The Denetrium Approach: Deploy in days with plug-and-play modules: begin with store checklists and expand into full enterprise internal audit and risk workflows as governance maturity deepens.
Bridge the gap between boardroom governance and frontline operations through built-in GPS geofencing, live camera capture, and tamper-proof audit trails.
Do not allow critical internal audit and risk processes to sit buried inside unencrypted spreadsheets or bloated software suites. Deploy Denetrium’s internal audit, mobile audit, and CAPA tracking ecosystem to enforce accountability from the boardroom to the front line.